M365 Tenant Architecture & Migration for Dallas-Fort Worth Businesses
For most Dallas-Fort Worth companies, Microsoft 365 is the operating system of the business. Email, files, identity, security, meetings, and increasingly AI all run through it. Yet a surprising number of organizations treat their M365 tenant as a switch that was flipped during onboarding — never architected, never governed, never optimized. That decision quietly taxes productivity and security every single day.
What M365 Tenant Architecture Really Means
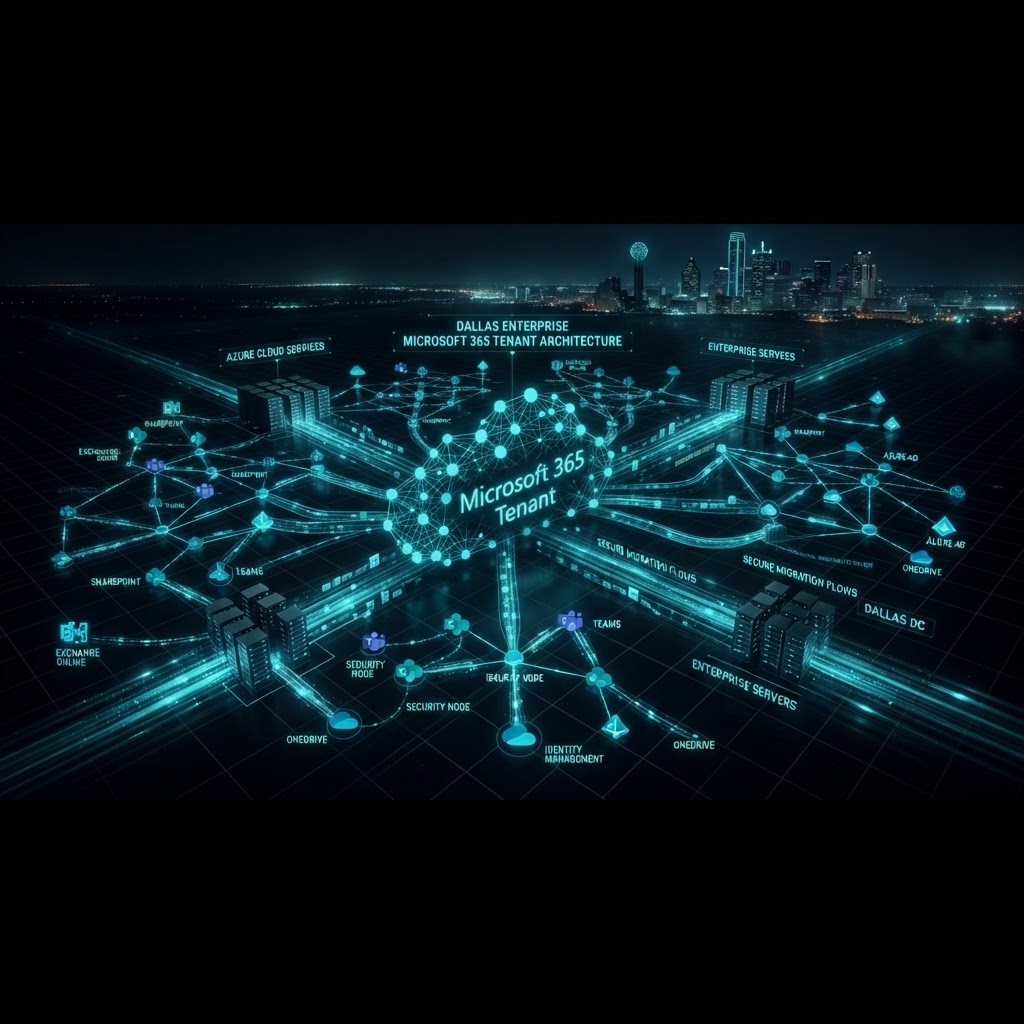
M365 tenant architecture is the deliberate design of how identity, data, security, and collaboration are structured inside your Microsoft 365 environment. It covers:
- Azure Active Directory (Entra ID) structure and conditional access
- SharePoint hub and site taxonomy
- Teams governance and naming policies
- Sensitivity labels and data loss prevention
- Defender, Purview, and compliance configuration
- Exchange routing and hybrid identity
When this is designed intentionally, people find what they need, data stays protected, and admins sleep at night. When it is not, you get permission sprawl, orphaned accounts, and shadow IT.
The Dallas-Fort Worth Reality
Dallas companies grow through acquisitions, rebrands, and rapid hiring. Each of those events tends to create a new M365 tenant — and suddenly the business is juggling two, three, or five separate identities. That is where tenant-to-tenant migration becomes essential.
Tenant-to-Tenant Migration: Get It Right Once
A tenant-to-tenant migration moves users, mailboxes, files, and Teams data from one M365 tenant to another without losing history or breaking access. Done poorly, it means weeks of broken logins and lost emails. Done right, it is a planned, zero-downtime event.
The proven Dallas-Fort Worth playbook:
- Discover and map every workload — mail, files, Teams, groups, Power Platform
- Coexistence planning so users keep working during the move
- Identity mapping with Azure AD as the source of truth
- Pre-stage and delta-sync so cutover is measured in hours, not days
- Post-migration cleanup — aliases, DNS, hybrid configuration, and licensing rationalization
Security Cannot Be an Afterthought
The moment you migrate or architect a tenant, you have a clean slate. That is the time to enforce:
- Multi-factor authentication and conditional access policies
- Least-privilege admin roles (PIM)
- Sensitivity labels and auto-labeling
- Legacy authentication block policies
- Audit logging and alerting
Why Pair Architecture with AI Automation
A well-architected M365 tenant is the foundation for AI automation. Copilot, Power Automate, and custom AI agents only perform well when your data is clean, labeled, and permissioned correctly. Dallas companies that skip architecture and jump straight to AI get unpredictable, sometimes unsafe results.
Partner with TERN
TERN (Technology Resource Nexus) designs and migrates M365 tenants for Dallas, Irving, and Fort Worth businesses that refuse to let their platform run on autopilot. Whether you need a from-scratch architecture or a complex tenant-to-tenant migration, we plan it, secure it, and execute it without the drama.
Start the conversation and let's build an M365 tenant that scales with your business.